Modern digital infrastructure relies heavily on mathematical encryption to protect financial systems, medical records, and global supply chains. For decades, standard cryptographic algorithms have effectively secured our digital economy. However, the rapid evolution of quantum computing threatens to undermine this foundational security layer.
Unlike traditional devices, a sufficiently powerful quantum computer will easily break current public-key encryption standards. This vulnerability leaves sensitive enterprise data exposed to unprecedented cybersecurity risks. To mitigate these future breaches, organizations must proactively initiate a migration toward quantum-resistant security, a domain known as Post-Quantum Cryptography (PQC).
Understanding the impact of quantum computing on modern cybersecurity is essential for maintaining long-term data protection. This article explores the threat vector posed by quantum devices and delivers a practical, step-by-step roadmap to transition your IT systems into a resilient, quantum-safe infrastructure.
Understanding the Quantum Threat to Modern Cybersecurity
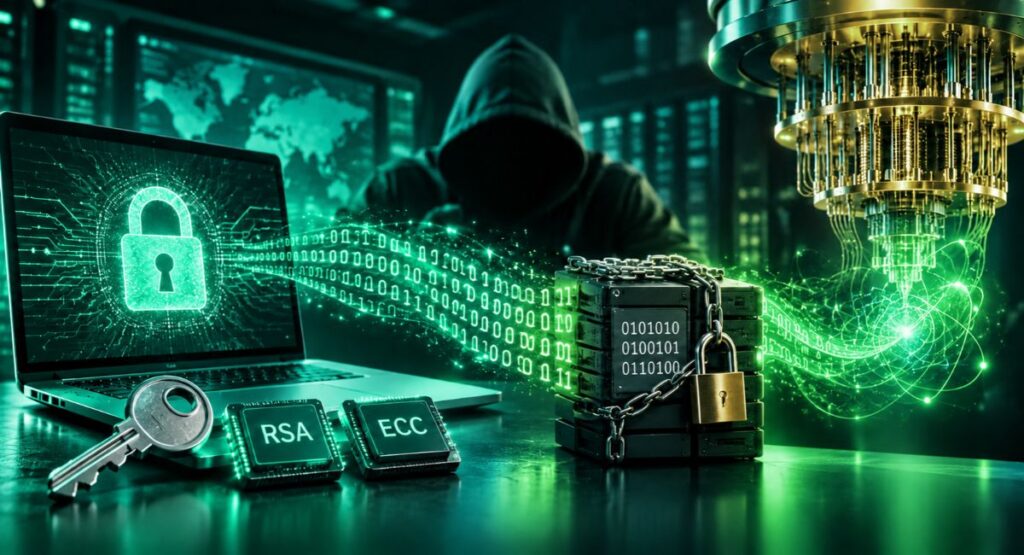
To shield your enterprise effectively, it helps to understand how traditional encryption operates and why quantum machines completely rewrite the rules of digital defense.
How Traditional Encryption Safeguards Our Data
Most modern security mechanisms rely on asymmetric encryption, also known as public-key cryptography. Common standards like RSA (Rivest-Shamir-Adleman) and ECC (Elliptic Curve Cryptography) secure everything from web traffic (HTTPS) to corporate VPNs and digital signatures.
These algorithms work because they rely on complex mathematical puzzles that standard computers find nearly impossible to solve. For example, factoring an extraordinarily large prime number using a traditional supercomputer would require thousands or even millions of years of continuous processing. Because the math takes an impractical amount of time to compute, your encrypted data remains safe.
Why Quantum Computing Shatters Classical Security
Traditional computers process information using binary bits, which exist as either a 0 or a 1. Quantum computers, in contrast, utilize qubits (quantum bits). Driven by fundamental principles of quantum mechanics, namely superposition and entanglement, a qubit can exist as a 0, a 1, or both states simultaneously.
This unique property enables quantum computers to run massive parallel calculations at astonishing speeds. A specific quantum mathematical shortcut known as Shor’s Algorithm can factor large prime numbers in hours or minutes rather than millennia.
When large-scale, fault-tolerant quantum systems arrive a milestone frequently referred to in the tech industry as Q-Day legacy public-key encryption standards like RSA and ECC will become vulnerable almost overnight.
The Immediate Threat: Harvest Now, Decrypt Later Attacks
A widespread misconception among business leaders is that quantum security is a future problem that can wait until commercial quantum supercomputers are widely available. Unfortunately, cybercriminals, espionage rings, and hostile actors are not waiting.
Through Harvest Now, Decrypt Later (HNDL) tactics, malicious actors are actively intercepting and storing encrypted data feeds today. Although they cannot read these encrypted files right now, they are hoarding the data until a quantum computer becomes accessible.
If your organization manages long-term sensitive assets such as customer identity records, proprietary research, financial transaction history, or government secrets, your data is already exposed to future decryption today.
Core Building Blocks of Quantum-Safe Defense
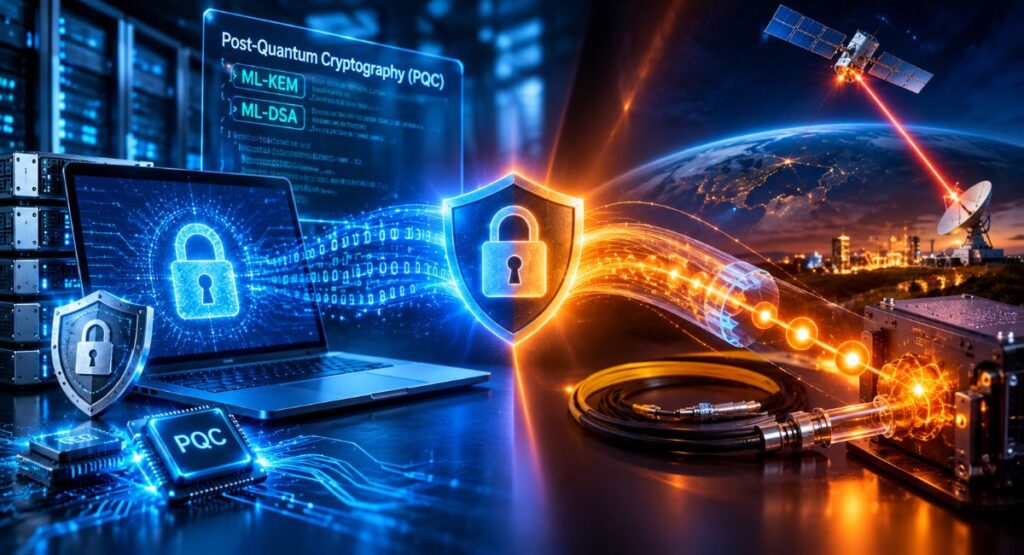
Transitioning an enterprise security posture is not as simple as installing a single software patch. It requires an understanding of the two principal approaches to quantum-resistant defense: Post-Quantum Cryptography (PQC) and Quantum Key Distribution (QKD).
| Security Dimension | Post-Quantum Cryptography (PQC) | Quantum Key Distribution (QKD) |
| Primary Mechanism | Software-based mathematical algorithms engineered to resist both classical and quantum attacks. | Hardware-based security using light particles (photons) over physical links to exchange encryption keys. |
| Primary Use Cases | Application updates, web browsing (HTTPS), VPN tunnels, identity management, and digital signatures. | High-security point-to-point communication channels (e.g., direct data transfer between central bank facilities). |
| Hardware Requirements | Operates on existing servers, cloud instances, and standard networking hardware. | Requires specialized optical equipment, dedicated fiber networks, and satellite receivers. |
Post-Quantum Cryptography (PQC)
Post-Quantum Cryptography centers on deploying new mathematical algorithms designed to run on standard computers and networks while remaining complex enough to resist quantum processing power.
Global standardization authorities, led by the National Institute of Standards and Technology (NIST), have spent years testing, auditing, and selecting robust PQC algorithms (such as ML-KEM for key encapsulation and ML-DSA for digital signatures). For the vast majority of commercial enterprises, adopting NIST-standardized PQC through software updates and firmware upgrades will serve as the primary path to quantum resilience.
Quantum Key Distribution (QKD)
Quantum Key Distribution leverages the physical properties of light particles to exchange cryptographic keys. If an unauthorized party attempts to intercept the quantum particles in transit, the physical state of those particles changes instantly, alerting both the sender and receiver to the interception.
While QKD offers unique physical security guarantees, it demands costly physical infrastructure, dedicated fiber optics, and geographic proximity limits. Consequently, QKD is primarily reserved for specialized environments such as military installations, critical energy grids, and primary financial settlement hubs.
A Practical Step-by-Step Roadmap to Quantum-Safe Infrastructure
Migrating an entire corporate IT ecosystem to quantum-safe standards requires strategic planning, clear prioritization, and consistent execution. The following five-step roadmap provides a clear path to guide your organization through a smooth migration.
Step 1: Discover and Inventory Your Cryptographic Assets
You cannot protect data that you do not know exists. The first stage of any quantum migration project is executing a comprehensive cryptographic discovery audit across your entire digital landscape.
- Map Your Data Repositories: Locate where sensitive data resides across local servers, private cloud environments, public cloud platforms, employee endpoint devices, and third-party vendor platforms.
- Catalog Encryption Algorithms: List every active encryption algorithm, digital certificate, cryptographic library, and protocol in use across your network connections and software stack.
- Track Application Dependencies: Document which internal applications, databases, microservices, and external APIs rely on these encryption algorithms.
Step 2: Assess Risk and Prioritize Vulnerable Systems
Not every digital asset demands immediate migration. You must rank your systems based on data longevity, operational impact, and regulatory requirements.
Work with your security and compliance teams to answer two critical questions for every system:
How long must this data remain secret?
If the required secrecy timeframe spans 10 to 30 years, it is vulnerable to Harvest Now, Decrypt Later attacks right now.
How long will it take to update or replace this system?
Upgrading legacy enterprise resource planning platforms or embedded devices frequently takes several years.
The Quantum Risk Formula:
If (Data Secrecy Duration) + (System Migration Time) > Estimated Time Until Q-Day, that asset is an immediate high-priority target for migration.
Step 3: Embrace Crypto-Agility
Historically, updating encryption algorithms across an enterprise required rebuilding application code and replacing hardware, a slow, expensive, and error-prone process. To prevent future operational disruptions, organizations must build crypto-agility into their IT architecture.
Crypto-agility is the structural capacity to swap encryption algorithms, modify key lengths, and update certificates without breaking underlying application logic or necessitating complete system redesigns. By isolating security protocols from core business code using modular design patterns, your development teams can seamlessly plug in updated post-quantum algorithms as global standards evolve.
Step 4: Pilot and Implement NIST-Approved Algorithms
Once your architecture supports crypto-agility, begin testing standardized PQC algorithms in controlled, non-production test environments.
- Deploy Hybrid Cryptographic Models
During the transition phase, implement a hybrid approach that pairs classical algorithms (like RSA) alongside post-quantum algorithms. This dual-layer strategy ensures that if a newly adopted post-quantum algorithm contains an unexpected implementation flaw, your classical encryption continues to provide a dependable baseline layer of security.
- Evaluate Network Performance and Overhead
Post-quantum encryption keys and digital signatures are significantly larger than classical counterparts. Controlled testing enables your network administrators to measure latency impact, memory consumption, and bandwidth demands before deploying updates to live environments.
Step 5: Establish Continuous Governance and Monitoring
Achieving quantum safety is not a one-off project; it is an ongoing operational commitment that must be integrated into your company’s long-term risk management strategy.
- Establish Vendor Requirements
Mandate that software partners, cloud hosting providers, and hardware suppliers provide clear quantum-readiness roadmaps and commit to PQC compliance.
- Upskill Technical Teams
Train software developers, system engineers, and network administrators on post-quantum secure coding standards and modern key management practices.
- Conduct Regular Security Audits
Schedule annual cryptographic reviews to detect unencrypted data paths, legacy certificates, or outdated communication channels.
Overcoming Common Transition Challenges
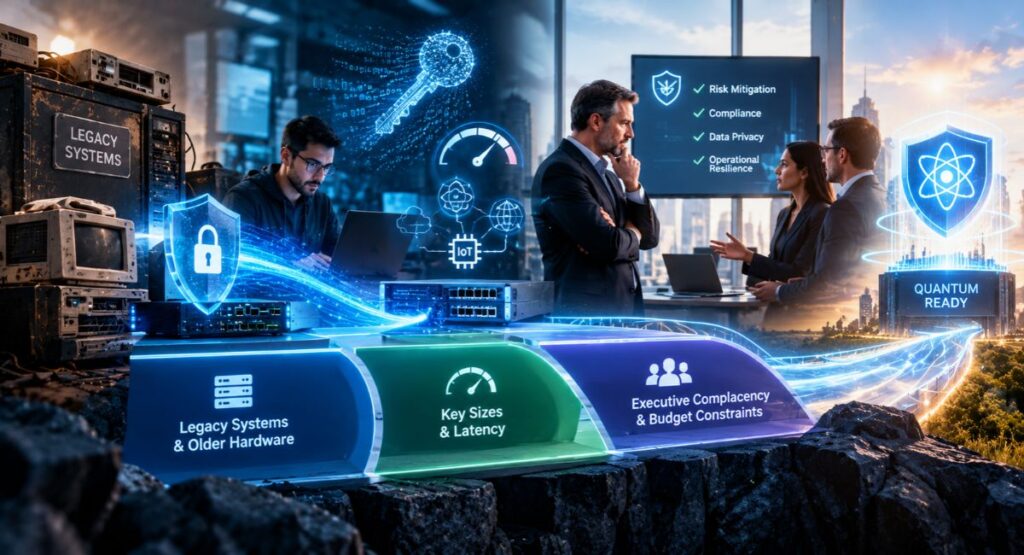
Every significant enterprise technology transformation encounters operational hurdles. Knowing what roadblocks to anticipate makes managing them significantly easier.
Challenge 1: Legacy Software and Aging Hardware
Many mature businesses rely on legacy applications that were never designed to accommodate modern security protocols or larger post-quantum keys.
Practical Solution:
Wrap legacy systems behind secure, crypto-agile gateway proxies. These proxy services isolate older applications from direct network traffic while handling outbound and inbound communications using modern, quantum-safe standards.
Challenge 2: Increased Key Sizes and Network Latency
Post-quantum algorithms rely on larger mathematical keys and expanded signatures. This extra data payload can slow down web application loading times, increase network overhead, and strain low-power IoT devices.
Practical Solution
Optimize network throughput and hardware utilization during your pilot testing phase. Conduct performance benchmarks across different NIST-approved algorithms to select the most bandwidth-efficient options for your specific network conditions.
Challenge 3: Executive Complacency and Budget Constraints
Because Q-Day can feel like a distant, theoretical concept to non-technical executive leadership, securing funding and executive sponsorship can prove challenging.
Practical Solution:
Frame quantum migration around active, measurable risks such as active Harvest Now, Decrypt Later threats, regulatory compliance standards, data privacy mandates, and operational resilience rather than theoretical future predictions.
Conclusion
The quantum computing revolution marks one of the most exciting technical evolutions in human history. Its ultimate success, however, depends entirely on our collective ability to fortify the digital foundation that powers our global economy.
Transitioning to a quantum-resistant posture cannot be executed at the last minute. By discovering your existing cryptographic footprint, embedding crypto-agility into your system architecture, and deploying NIST-approved post-quantum algorithms today, you can ensure your business remains secure, resilient, and prepared for the future of computing.